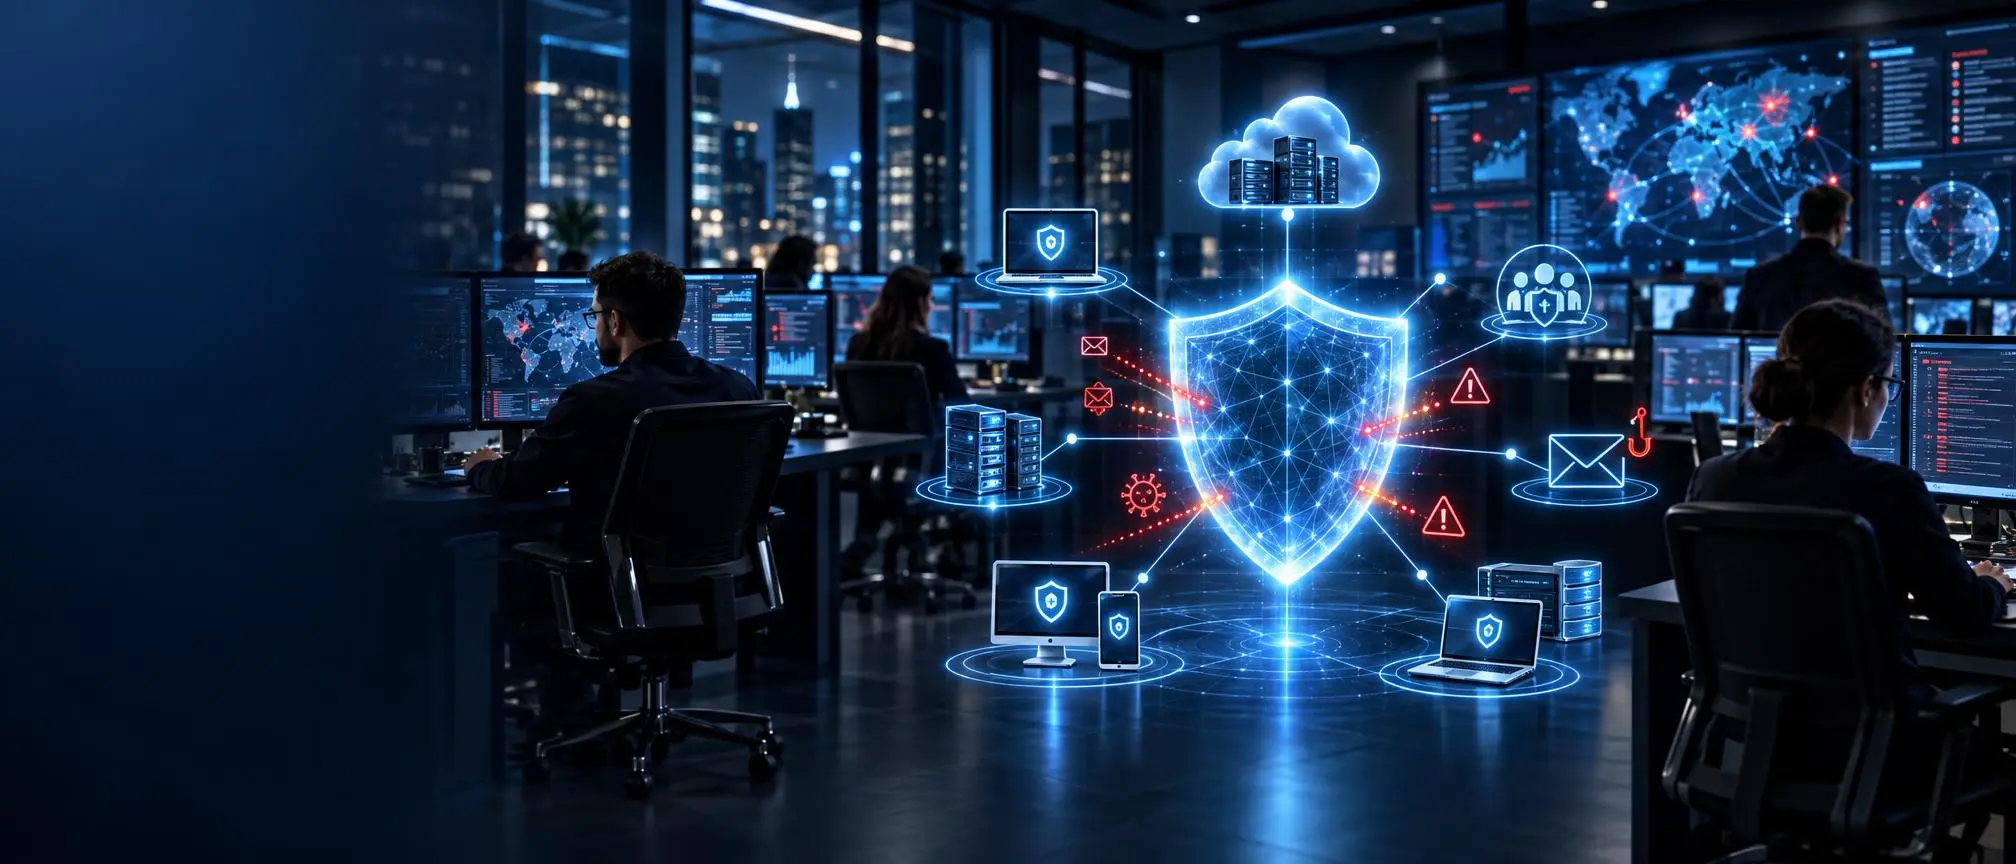

In today’s environment, cybersecurity as a service (CSaaS) is essential for businesses of all sizes looking to protect against cyber threats.. Businesses of all sizes including small businesses, emerging companies, e-commerce sites, healthcare organizations, professional services providers and remote teams use digital technology and are vulnerable to cyber-attacks such as phishing, malware, ransomware, identity theft and others. It is however difficult for many organizations to build an internal security team due to costs and management.
The use of cybersecurity as a service (CSaaS) can assist organizations who are unable to purchase all of the necessary security tools individually, as well as hire specialized staff to perform the individual tasks. Businesses can utilize an outside vendor to provide continuous security capability via either a subscription or managed services contract. Vendors providing CSaaS will typically provide ongoing system monitoring, investigation into potential threats, management of vulnerability issues, incident response assistance, and support for regulatory compliance.
What Is Cybersecurity as a Service?
CSaaS (cyber security as a service) is a model where organizations use the expertise of external providers for their cyber security needs. Rather than having all functions performed within the organization, CSaaS allows for these functions to be outsourced.
External vendors manage threats, endpoints, vulnerabilities, identities, clouds, and incidents. This allows companies to maintain strong security without high internal costs.
External service agreements provide organizations with security experts, tools, and processes. Companies skip building large internal security teams while maintaining strong protection.
How Does Cybersecurity as a Service Work?
Cyber security as a service usually starts off by conducting a thorough examination of your organization’s environmentThe provider evaluates all devices, accounts, networks, apps, cloud systems, and existing security tools. Analysts also review previously identified vulnerabilities.
The typical process looks like this:
- Security data comes from endpoints, cloud services, network, identity and app.
- Alerts and unusual activity are analyzed.
- Potential threats are investigated and prioritized.
- High-risk events are contained or escalated.
- Vulnerabilities and security gaps are reported.
- Recommendations are provided to improve the organization’s security posture.
- Reports and metrics are shared with management or IT teams.
These activities will depend on which service you choose to useService providers combine automated systems, AI, and human analysts to perform security functions. Providers also deploy specialized security software to protect client data.
Core Services Commonly Included in CSaaS
Businesses need to understand that not all cybersecurity as a service (CSaaS) providers offer identical packages. Choose a CSaaS provider based on their specific service offerings rather than relying solely on the label.
Continuous Security Monitoring
Continuous monitoring is useful for identifying abnormal actions on systems, networks, clouds, and individual user accounts.
Providers can maintain a Security Operations Center (SOC) with their security analysts monitoring for alerts and investigating possible security threats.
Managed Detection and Response
Managed detection and response, or mdr, is about finding and dealing with current threats.
The security analyst reviews the alert, investigates the suspect activity and takes measures to prevent the spread of the malicious activity. MDR is usually a critical part of a larger cybersecurity as-a-service program.
Vulnerability Management
Outdated software, incorrect configurations, weak credentials, exposed services, and cloud changes create security vulnerabilities. Businesses can fix these weak spots through active management.
Vulnerability management identifies weaknesses, ranks their risk levels, and recommends fixes. Companies can quickly prioritize and resolve security gaps.
Endpoint Security
Attackers often target computers (such as laptops, desktops, etc.), servers, and other types of connected devices.
CSaaS providers can assist in managing Endpoint Detection and Response tools, Anti-Virus software, Device Security Policy, and Threat Containment processes.
Cloud Security
Companies increasingly rely on cloud services, remote storage, SaaS apps, and collaboration tools. These digital platforms support distributed teams while expanding the corporate attack surface.
Providers monitor cloud settings, access rights, login attempts, and suspicious user behavior. This active oversight quickly blocks unauthorized access.
Email and Identity Protection
Attackers use phishing emails and stolen account credentials to try to gain access to an organization’s computer network.
Providers secure email accounts, deploy multi-factor authentication, monitor login attempts, and strengthen user access control.
Incident Response Support
When a serious security event occurs, organizations need a structured response.
Incident response teams investigate attacks, contain affected systems, and limit damage. Experts recover normal operations and improve security to prevent future breaches.
Compliance and Security Reporting
Organizations operating within regulatory environments may be required to document their organization’s policies, security controls, risk assessments, reports, and audit trails.
Compliance advice and reporting is included in some of the as-a-service offerings of many cyber security firms.
Key Benefits of Cybersecurity as a Service
A key benefit of using Cybersecurity-as-a-Service is that you have access to expert cybersecurity professionals, without having to build out an entire, internal security team.
Lower Operational Burden
Cybersecurity applications need to be configured, monitored, maintained, investigated and updated on a consistent basis.
The use of third-party vendors for some security responsibilities may help ease the burden that is being put upon your internal IT staff so that they are able to focus more on strategic objectives within your organization.
Access to Specialized Skills
Cybersecurity includes many different disciplines.
An internal team that is relatively small may not be able to hire specialists who are experts in threat hunting, cloud security, identity management, incident response, malware analysis, vulnerability management and compliance.
Using a managed service provider provides an organization with a wider selection of skill sets.
More Predictable Costs
Many cybersecurity as a service providers employ either a subscription-based model or a contractual agreement for their pricing structure.
Cybersecurity spending can be more easily predicted than when a company hires numerous full time specialists and buys several security platforms separately.
Faster Security Expansion
As a company expands, they will likely have to protect more of their workforce, equipment, cloud environments, applications, and physical sites.
Managed security models can provide a way for an organization to increase their level of security protection as they grow, and avoid having to rebuild the organization’s existing security infrastructure with each change to the organization.
Continuous Coverage
Cyberattacks are not limited to normal business hours.
Providers monitor systems and networks 24/7. This continuous oversight protects operations while internal staff are off duty.
Cybersecurity as a Service vs. MSSP
In general terms, a Managed Security Service Provider (MSSP) typically provides customer-specific management of certain types of security technology and/or operations.
MSSPs manage firewalls, utilize security information and event management tools, monitor network traffic, and respond to alerts.
Cybersecurity as a service may have a wider reach. It could incorporate monitoring, threat detection, incident response, vulnerability management, governance, cloud security, compliance support, and strategic security support into one service model.
However, terminology varies between vendors.
Businesses need to look at what the vendor is providing, rather than assuming that all companies offering CSaaS and/or MSSP services are providing the exact same thing.
Cybersecurity as a Service vs. MDR
Managed Detection and Response has a more specific purpose, as detailed in this guide on MDR vs SOCaaS
MDR is primarily concerned with identifying, investigating, and reacting to security threats.
Cyber security as a service functions as an MDR option while offering a broader scope. Providers deliver prevention, governance, vulnerability management, identity security, compliance, employee awareness, and cloud protection.
The correct choice will be based upon what security measures are currently in place at an organization and what areas require improvement.
Who Should Consider CSaaS?
Cyber security as a service can be beneficial to organizations of all sizes, however, it may be especially helpful for organizations that are seeing their cybersecurity needs increase at a much faster rate than they can handle internally.
It may be suitable for:
- Small and medium-sized businesses without dedicated cybersecurity departments.
- Startups experiencing rapid growth.
- Companies with remote or hybrid workforces.
- Businesses moving important workloads into the cloud.
- Organizations that deal with customer data, payments, financial records and/or other forms of confidential data.
- Companies facing new security or compliance requirements.
- IT departments that are overloaded with operational tasks.
- Organizations requiring continuous monitoring without building an internal SOC.
Companies can pair CSaaS with existing security personnel. Therefore, organizations do not need to replace their current internal teams.
How to Choose a Cybersecurity as a Service Provider
When choosing a cybersecurity as a service provider, you need to consider this a major business risk decision, not just another software purchase.
Providers explain what happens after identifying an attack. Vendors detail quarantine steps, account access removal, investigation support, and recovery assistance.
Will the provider just notify me? Are the provider’s analysts able to quarantine a system after infection? Are the provider’s analysts able to remove access to compromised accounts? Do the provider’s analysts provide assistance during the investigation process following an incident and during the recovery phase?
Businesses should also evaluate:
- Services included in the contract.
- Hours of security monitoring.
- Incident response procedures.
- Supported cloud platforms.
- Integration with existing security tools.
- Data privacy practices.
- Reporting frequency.
- Relevant certifications and experience.
- Service-level agreements.
- Escalation procedures.
- Pricing structure.
- Additional charges.
- Customer support.
- Response times.
A qualified professional will use clear and concise language when explaining their duties and processes.
Software license and dashboard based services do not offer the support levels that a fully managed security operation would.
Potential Limitations to Consider
Cybersecurity as a Service (CaaS) offers many benefits, however, using CaaS doesn’t relieve organizations of their own security obligations.
The need for companies to have effective cybersecurity measures has not changed. This includes but is not limited to: strong passwords, multi-factor authentication, staff knowledge of cyber threats, access control of users, regular updates to all software, backups that can be accessed securely, and established lines of authority regarding internal decisions made about security.
Vendor dependence is another factor to consider.
Third parties handle sensitive information and access critical resources, so companies must understand how vendors manage and protect data. Organizations track data maintenance, employee access permissions, processing methods, and contract termination protocols.
Companies will want to determine the level of access that a company has to its systems in the event of an incident. Some agreements allow for automated containment of suspicious activity, while other agreements require customers to authorize any containment actions taken by analysts.
These details can significantly affect response time.
Is Cybersecurity as a Service Worth It?
As an alternative for organizations seeking to improve their security posture and who do not have the resources to establish a full internal cybersecurity program, cybersecurity-as-a-service may be a viable option.
It will enable businesses to have the advantage of having professional monitoring of their security systems, access to specialized expertise in the area of security, an organized approach to managing security operations, the ability to manage vulnerabilities within their network, and the capability to respond to incidents.
Value is based upon the quality of the provider as well as the alignment of the service with the true risk of the organization.
An online business that is relatively small will generally require protection for endpoints, email, identity, and ransomware. On the other hand, an organization that is larger and operates across several cloud platforms will usually require continuous monitoring, vulnerability management, incident response capabilities, compliance support, and security governance.
Before you request proposals, knowing your requirements will help you compare different providers.
Frequently Asked Questions
What does cybersecurity as a service mean?
Cyber security as a service (CSaaS) involves organizations getting access to their cyber security needs via a third-party organization that provides those needs as a regular part of a managed service or subscription model. CSaaS providers monitor threats, detect active attacks, and respond to breaches. Vendors also manage network vulnerabilities, secure endpoints, deliver cloud protection, and assist with compliance requirements.
Is cybersecurity as a service suitable for small businesses?
Small businesses may also benefit from CSaaS as many do not have the ability to run an entire internal cybersecurity team. Managed service providers provide access to specialist knowledge and security monitoring based on what package you purchase.
Is CSaaS the same as an MSSP?
Businesses need to compare the specific services offered by each provider, rather than just the name, because there are no clear definitions of what an MSSP does versus what a CSaaS does. MSSPs typically manage some subset of a business’s security systems, or monitor them. CSaaS covers a larger set of capabilities related to cybersecurity.
Does CSaaS include 24/7 monitoring?
Cybersecurity as a service providers may provide 24/7 monitoring, however, this service may not be included in each of their plans. Prior to selecting a plan, verify the provider’s monitoring hours, time to respond to incidents, how they escalate issues, and the availability of analysts.
Can cybersecurity as a service prevent every cyberattack?
No. There isn’t any type of cybersecurity product that can prevent all attacks. The goal of CSaaS is to lower the probability of being attacked, detect threats sooner, allow for quicker reactions, and minimize the damage caused by security breaches.
How much does cybersecurity as a service cost?
Universal Pricing does not exist. The cost is dependent upon the total amount of user accounts/devices to be monitored, the type of monitoring required (e.g., continuous), whether the organization has a cloud-based environment(s), what compliance standards need to be met, if incident response services will be provided, the types of security technologies that are currently in place or planned for implementation, and ultimately how complex the overall system is. Organizations need to request a detailed breakdown from each potential vendor regarding recurring fees and any other charges associated with using their service.
Final Thoughts
Organizations often struggle to hire and retain highly trained cyber security professionals, even though their networks have grown more sophisticated.
The “managed model” will provide a solution to this problem with its combination of security technology, expertise, monitoring and operations support.
Cyber security as a service provides businesses with an alternative to improving their security posture without having to purchase each security solution individually or employ experts to handle each function.
Before selecting a provider, organizations must review deliverables, incident handling protocols, internal responsibilities, pledged response times, and infrastructure integration.
The objective of the organization’s purchasing decisions is not merely to obtain additional security technology. Rather, the primary objective is to develop a security model that will provide greater visibility, reduce the amount of risk the organization can manage, and establish a well-defined procedure for addressing issues as they arise.